Why third-party risk belongs on rails, not negotiations
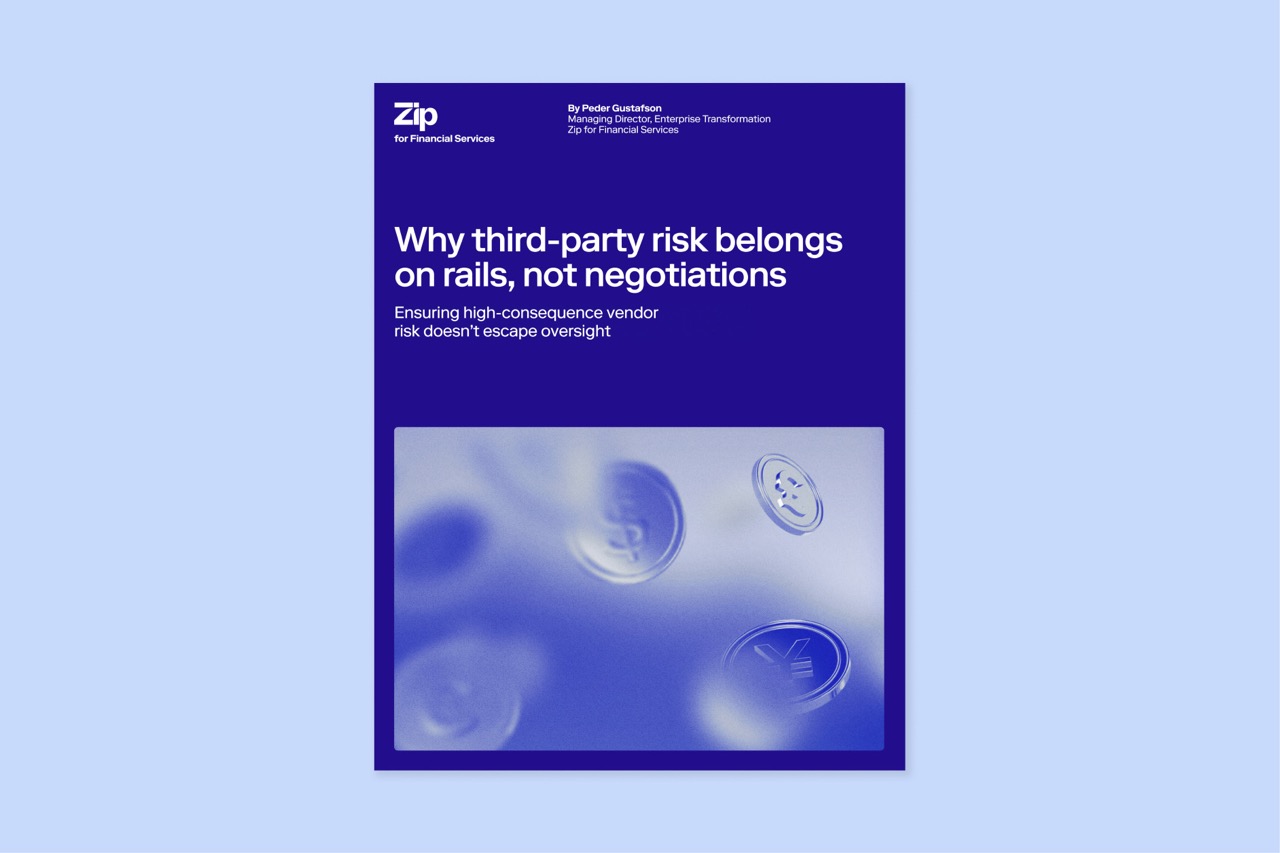
Most TPRM failures start on the day a business unit signs a vendor that risk never reviewed. The review work then spreads across email threads and GRC tools that don’t share data, and the exposure surfaces months later as an audit finding.
In this guide, Peder Gustafson, Managing Director of Enterprise Transformation at Zip for Financial Services, explains how to put intake, assessments and approvals on one path that every vendor engagement has to follow.
What’s inside
- How an unvetted vendor turns into an audit finding, and where the process breaks along the way
- Five moves for building controls into intake, assessments and lifecycle monitoring
- How orchestration runs on top of your existing ERP and GRC systems, including in multi-entity organizations
- A crawl-walk-run rollout that starts with a single high-risk business unit
- Where probabilistic AI helps, and why assessments and approvals need deterministic AI that examiners can audit
Written By

Thank you
Please check your email to access your download.
Thank you for registering for our upcoming webinar. Please check your email for your confirmation email.
Related resources
Webinar
Live demo: AI agents for AP Automation
Explore where AI spend actually fits into your workflow and how agents can help finance.